

Financial law
DORA compliance: legal implementation and ICT contract review
DORA links ICT risk management, incidents, testing and relationships with technology suppliers. For DORA compliance, the legal documentation must reflect how the institution actually operates. For a software supplier, it is also necessary to distinguish the client's contractual requirements from direct regulatory scope.
4,872 reviews on Google
CZK 50 million professional liability insurance
You know the price in advance
Mlčenlivost podle § 21 zákona o advokacii
At least two lawyers on every case
DORA: ICT resilience
Scope, suppliers, incidents and responsibilities
Our lawyers
Who will handle your case
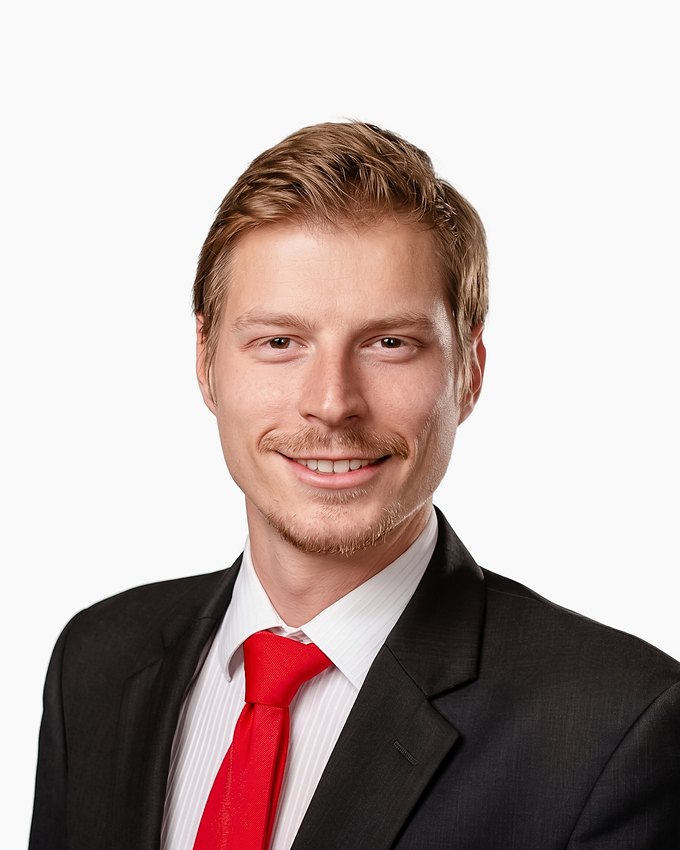
Two lawyers work on every case, so you always know who you are dealing with, even when one of them is at a hearing.
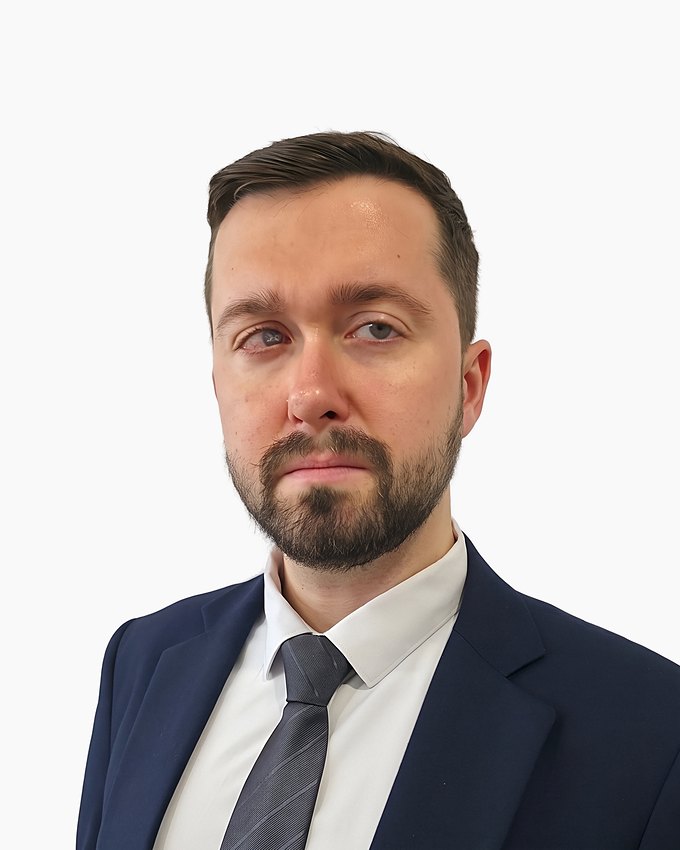
Mgr. Oleksandr Spitsyn
Attorney · 6 years' experienceCzech Bar reg. no. 21443View profile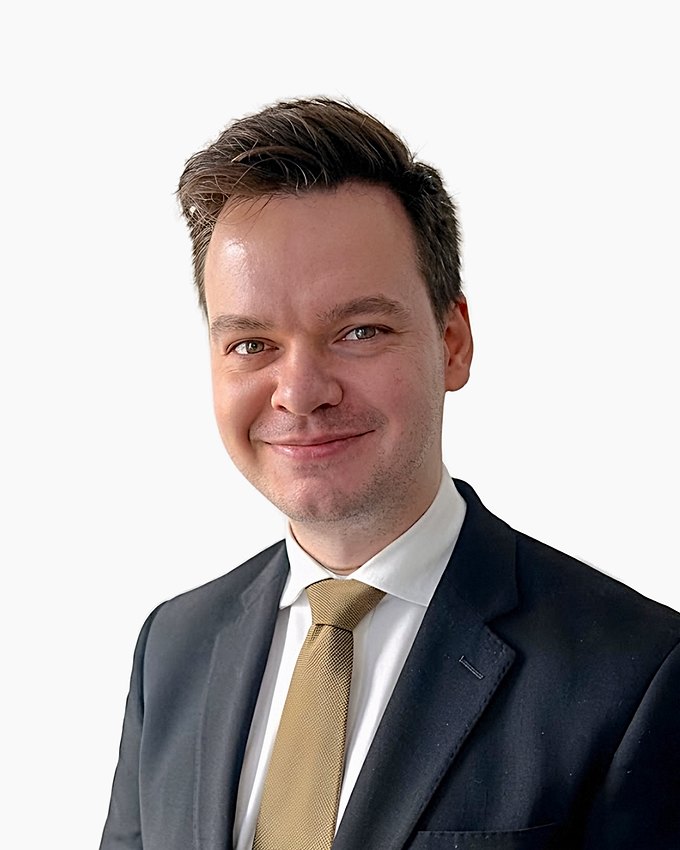
Mgr. David Imre
Trainee attorney · 4 years' experienceCzech Bar reg. no. 45923View profileSteps
How we work together
- 1We establish whether you are a financial institution or an ICT supplier and request the contracts and service descriptions.
- 2We assess the legal gaps and propose revisions.
- 3Technical testing and security configuration are handled by the appropriate specialists under a separate scope.
Worked example
An illustration, not a client case
1
2
This illustrates how we work. It is not a documented case handled by the firm or a promise of any outcome.
Fees
Clear fees. No surprises.
We set the fee according to the scope and complexity of the work and confirm it in a written quote before we start. Work beyond the agreed scope is billed only with your prior approval.
Initial assessmentFREEvia online chat
Hourly rateCZK 4,000+ VAT
Prices are indicative and exclude VAT. Unless expressly agreed otherwise, court, administrative and notarial fees, insurance premiums and external expert reports are not included.
Practical checklist · 6 pointsWhat to prepareOpen checklistClose checklist
List the ICT services and contracts
Identify the functions supported
Map the subcontractors
Describe incident escalation
Prepare the exit and data migration
Separate legal and technical tasks
Reviews
What our clients say
Excellent 4.8 72 reviews on GoogleWrite a review
They helped me with very good advice on how to run my projects. The consultation was scheduled very fast and talk was very professional.
Very efficient and professional, the problem is with the czech police but the lawyers are excellent would recommend
I highly recommend this law firm. Together we dealt with a criminal matter in which I was the injured party. Thanks to their human approach and willingness… (translated from Czech)
The firm handled my employment dispute and I was very satisfied. In the end the whole matter was settled out of court… (translated from Czech)
Frequently asked questions
Frequently asked questions
Didn't find your answer? Message us in the chat. The initial case assessment is free.
Ask in the chatPrepare a list of ICT services, the contracts including annexes, and information on which of the institution's functions they support. We check data rights, incident cooperation, audit, subcontractors and termination of the service. For services supporting critical or important functions, we review the enhanced requirements and how they tie in with internal risk management.
The bank may need contractual commitments on service availability, security, incidents, audit, subcontractors and the return of data. The requirements should reflect the nature of the service and its importance. We review their legal scope and how far they can be negotiated; separately, we assess whether you are an ordinary ICT supplier or fall under a different, direct regulatory regime.
Write down the specific gaps and ask for an appropriate contractual solution. At the same time, assess how important the service is, the options for remediation and whether an alternative supplier is available. For critical dependencies, prepare a realistic transition and exit plan. A refused clause is not dealt with simply by signing a risk statement; the institution must still meet its applicable obligations.
Our blog
Articles on financial regulation
Finance and investment7 July 2026 · 4 min read
Finance and investment7 July 2026 · 4 min read
Finance and investment23 June 2026 · 3 min read
Get in touch
What happens next
- 1We assign your matter to a specialistBased on the area you choose in your enquiry.
- 2We get back to you within 24 hoursOn working days, by phone or email.
- 3You receive a plan and a priceIn writing, before any work begins.